Assessments with a written scope
Every assessment starts with agreed scope and rules of engagement: which systems, which environments, which hours and who to call if something looks wrong.
Security assessments and penetration testing of web, API and mobile apps, hardening of cloud, servers and API gateways, and data protection aligned with Kenyan law.
Every assessment starts with agreed scope and rules of engagement: which systems, which environments, which hours and who to call if something looks wrong.
Penetration testing of web, API and mobile applications, looking for the weaknesses attackers use: broken access control, injection, weak authentication and exposed data.
Secure configuration of cloud accounts, Linux and Windows servers, databases and API gateways, including WSO2 API Manager, checked against recognised hardening benchmarks.
Secure development practices for your teams: threat modelling, code review, dependency and secret scanning, and security tests in the CI pipeline.
A review of how you would detect, contain and recover from an incident: logging, backups, access, contacts and who decides what, before you need it.
Practical controls and records aligned with the Kenya Data Protection Act 2019: what personal data you hold, where it goes, who can see it and how long you keep it.
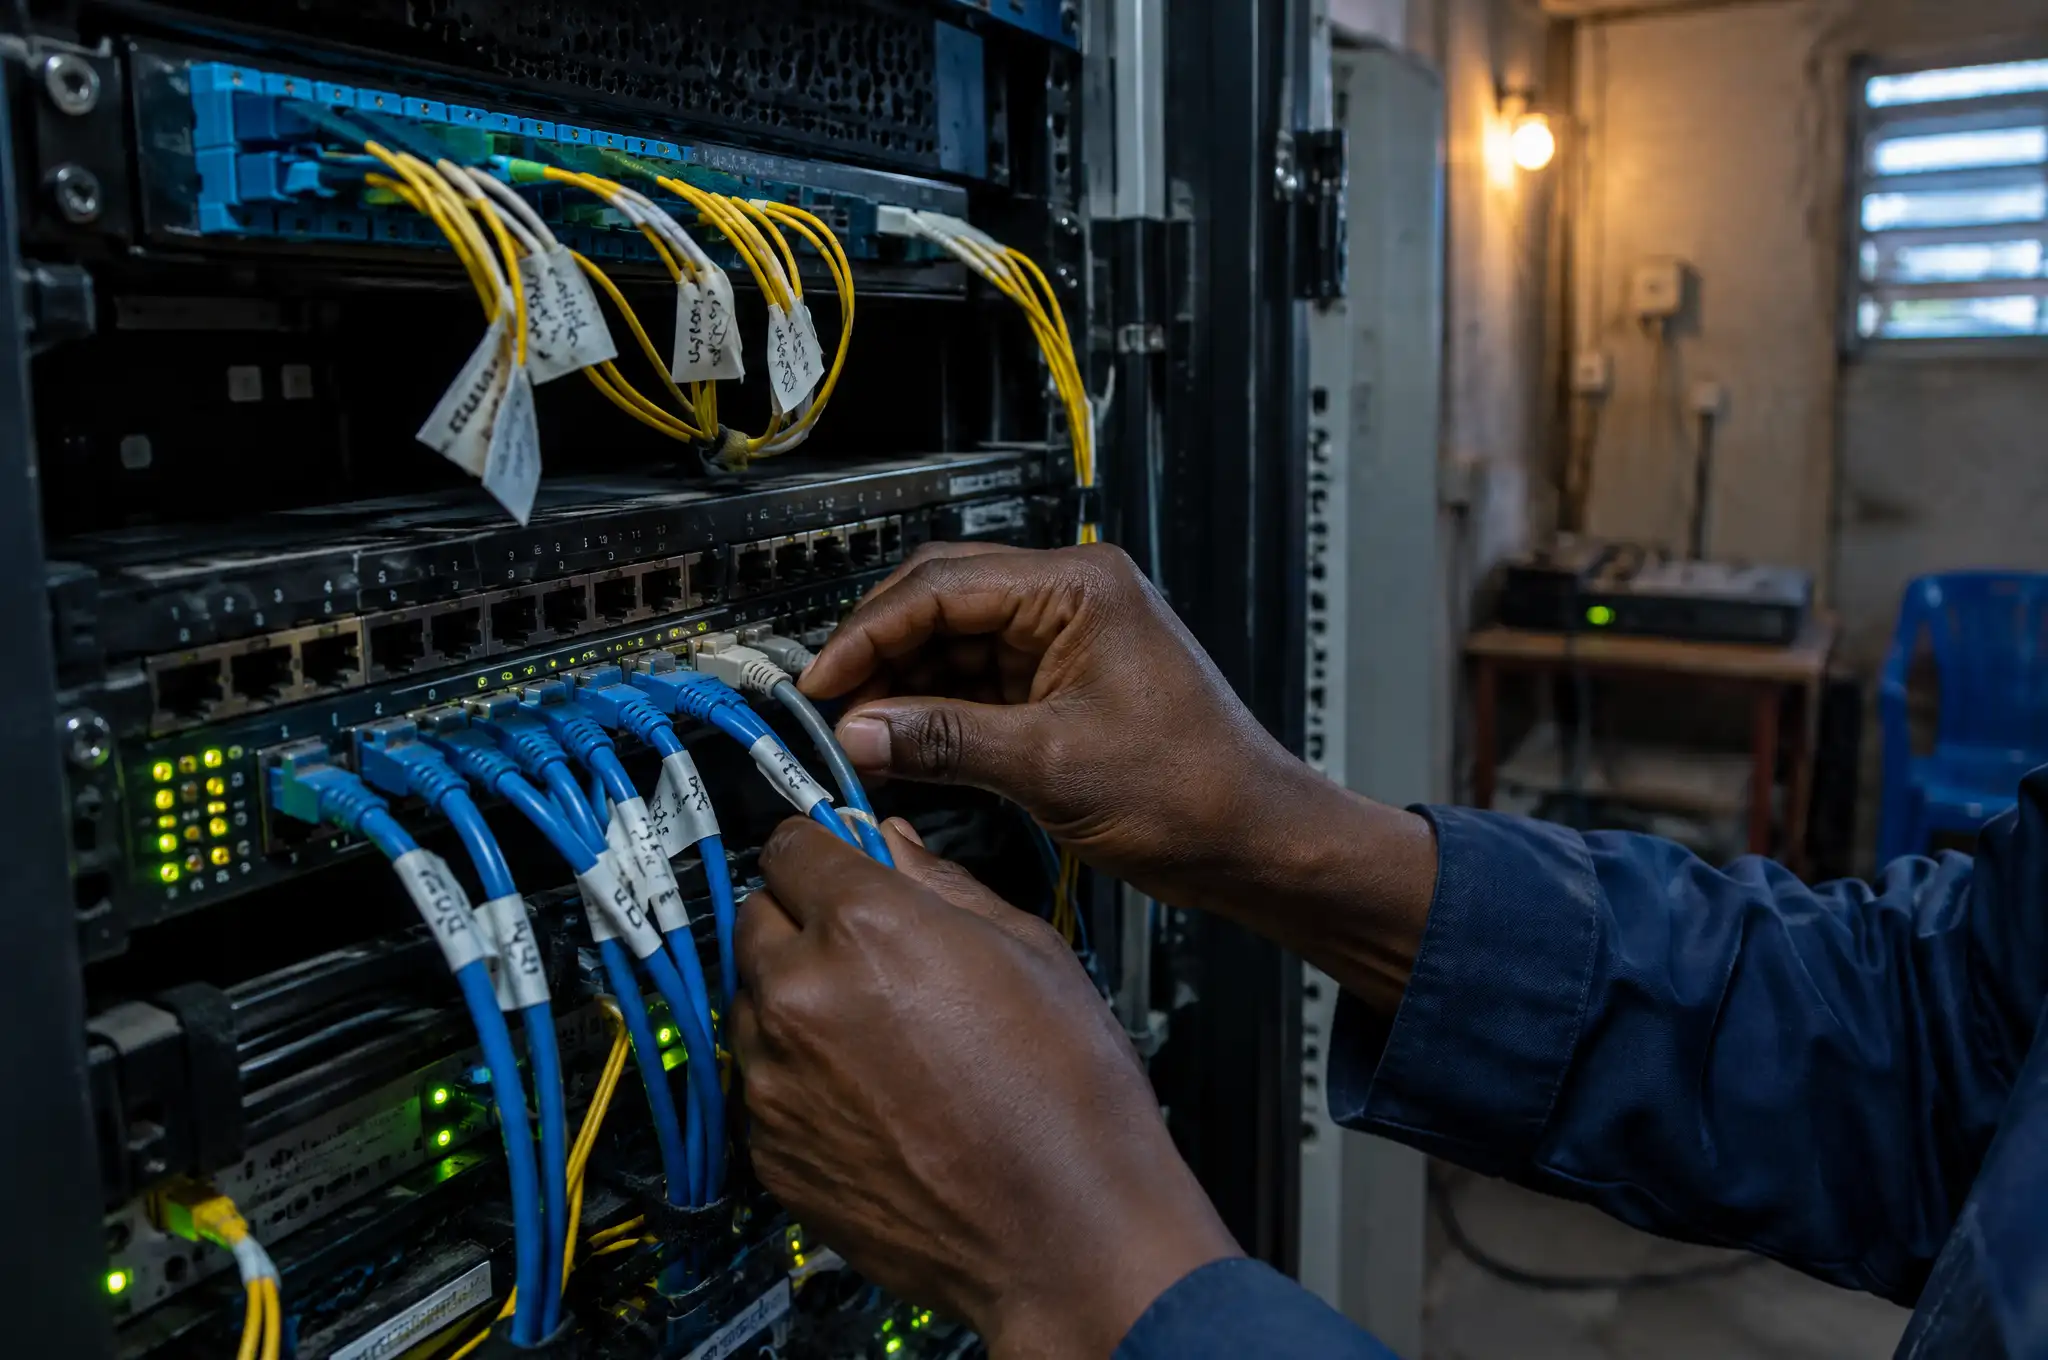
Vulnerability scanning, penetration testing and configuration review of your applications, APIs, servers, cloud and gateways, with findings ranked by risk.
Vulnerability scanning and a review of your applications, servers and cloud configuration, with findings ranked by risk and a remediation plan.
Manual and tool-assisted testing of web, API and mobile applications within an agreed scope, followed by a retest once fixes are in.
Secure configuration of cloud, servers and WSO2 gateways, and secure development practices built into how your teams ship.
Few breaches start with something clever. They start with an API that returns another customer’s records when an ID is changed, an admin route that was never meant to be public, a server still on its default configuration, or a password that a former employee still knows.
These are findable. The work is to look for them methodically, fix them in order of risk, and keep them from coming back with the next release.
What you receive depends on the scope you agree with us.
The findings report is written for both your engineers and your management. It has four parts:
Most of the systems we see in banking and payments are now reached through APIs. We have published a payment gateway’s APIs through WSO2 API Manager, so we know where gateways are usually left open: published administrative routes, back ends that trust a header instead of a signed token, and one set of credentials shared by every caller. A gateway review checks each of these. See Integrations for how we build them.
Security keeps attackers out of your systems. Transaction monitoring watches what happens to the money inside them. For banks, SACCOs and payment providers the two belong together. See AML & fraud detection and IntegWatch, our financial crime intelligence product, now onboarding early-access partners.
A security assessment reduces risk; it cannot remove it. We report what we tested, what we found and what we did not test, so your board and your regulator see an honest picture. Compliance decisions stay with your institution; we give you the evidence and the fixes.
Tell us which systems, APIs and gateways are in scope, and what is driving the review. We agree written scope and rules of engagement with your IT and risk teams before any testing starts.